Operational Protocol: The ‘Forge’ Provisioning & Fulfillment Manual
1. Operational Context and Strategic Mission
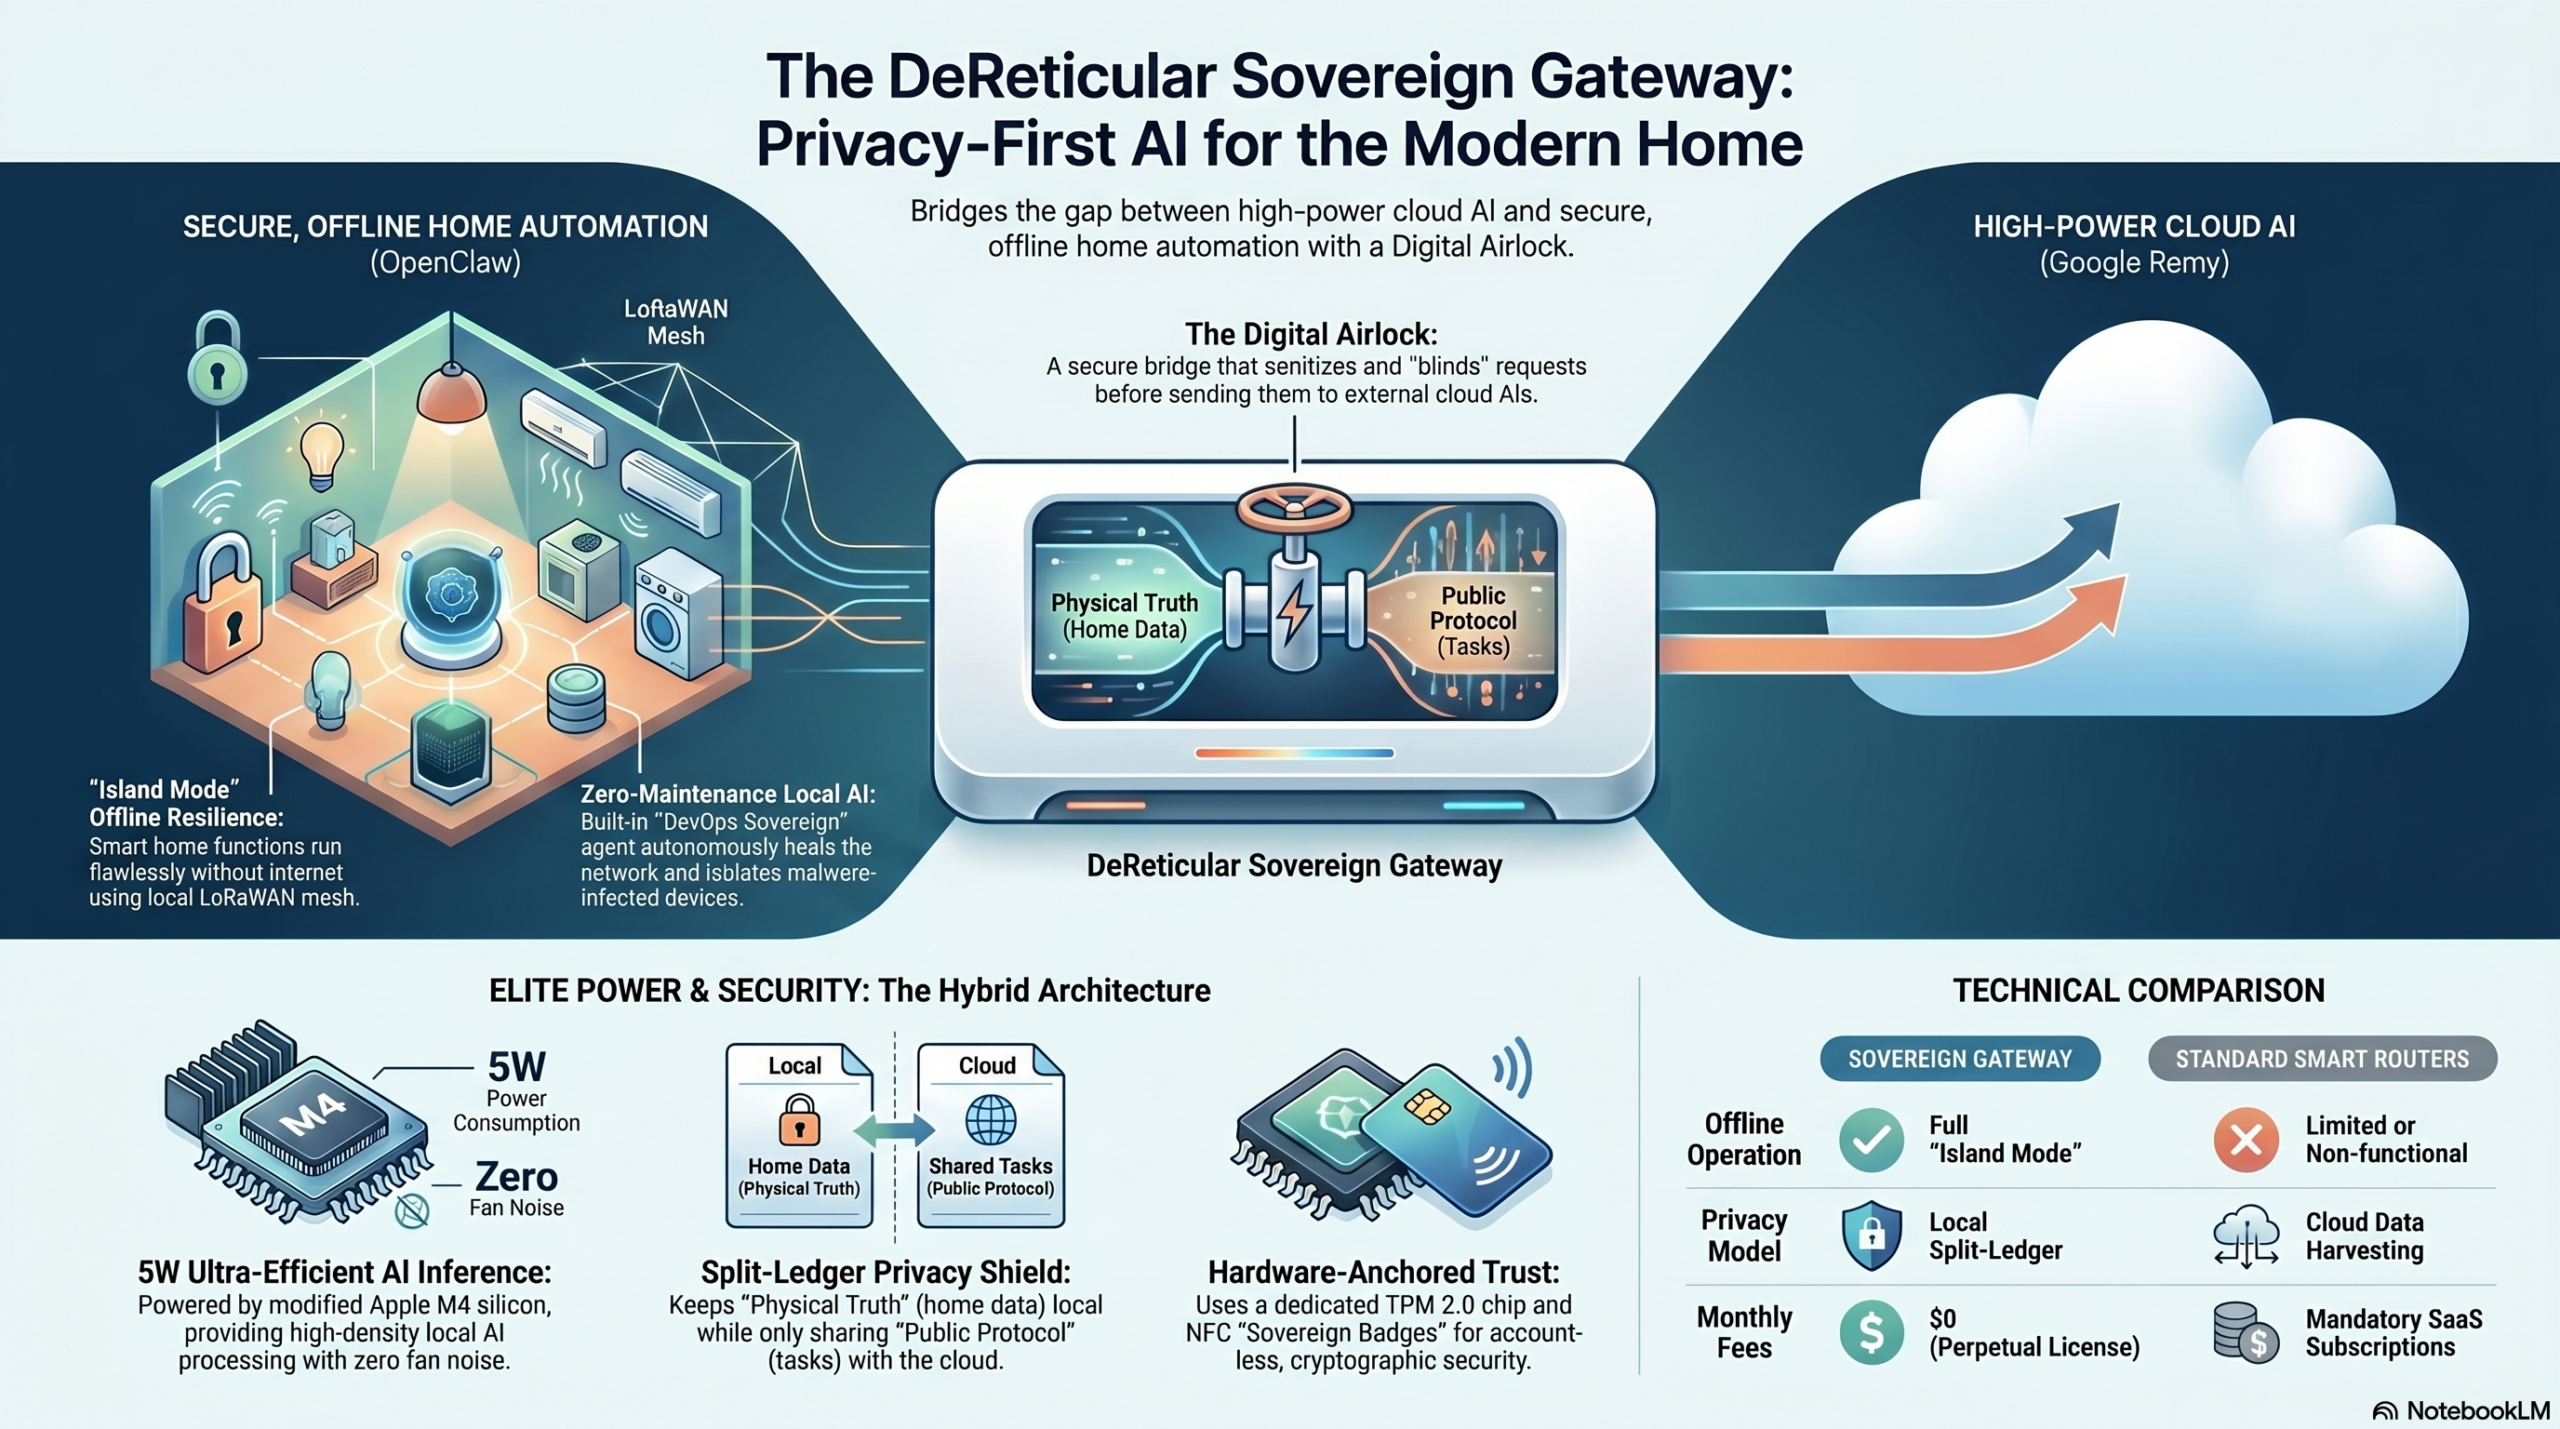
In the 2026 “Agentic AI” landscape, the Sovereign Gateway represents the definitive defensive pivot against centralized, invasive telemetry harvesting. As corporate entities like Google deploy “Project Remy” to maintain 24/7 proactive surveillance under the guise of convenience, DeReticular’s commitment to “Island Mode” and trustless infrastructure provides the only viable sanctuary for digital sovereignty. This manual mandates a rigorous, high-security fulfillment protocol to ensure that every node entering a consumer’s home is a cryptographically sealed fortress. Technicians must understand that our “Spherical Resilience” begins here; any deviation from this protocol compromises the air-gapped integrity of the end-user’s environment.
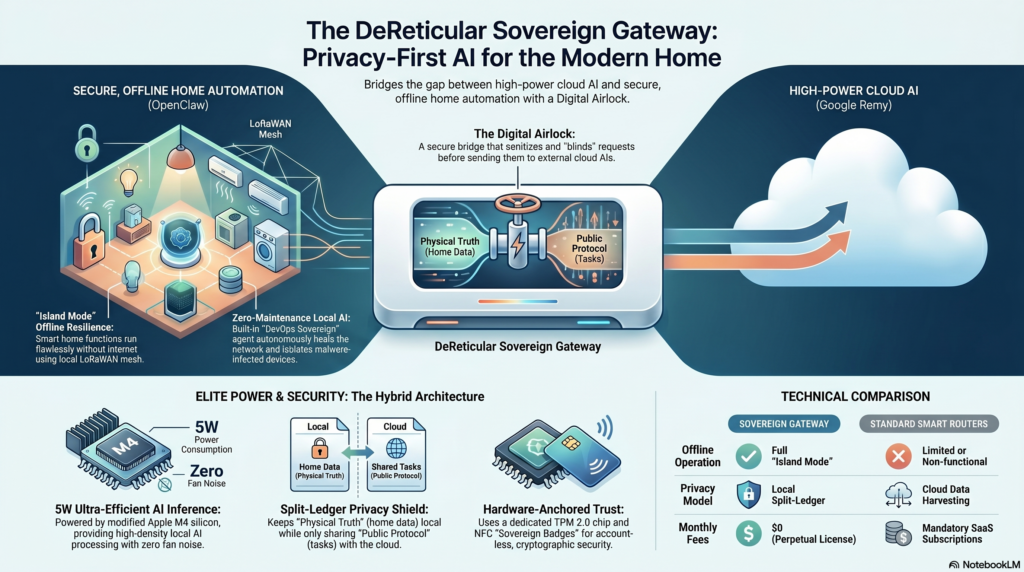
Core Value Proposition Synthesis
Technicians shall ensure all fulfillment activities support these four operational pillars:
- Island Mode: Offline resilience where smart home and mesh operations function without external internet.
- Zero-Maintenance IT: Local AI agents autonomously heal networks and neutralize threats.
- Trustless Cloud Integration: The “Digital Airlock” sanitizes external requests to cloud AIs (e.g., Google Remy) via the Split-Ledger Privacy Shield.
- No SaaS Subscriptions: Perpetual licensing model; the user owns the hardware and local AI capability in perpetuity.
Terminology Alignment
Adherence to the following glossary is mandatory for all warehouse and provisioning personnel:
| Term | Definition |
| Agentic AI | AI capable of executing autonomous, multi-step tasks rather than simple text generation. |
| DePIN | Decentralized Physical Infrastructure Networks; the core industry for DeReticular infrastructure. |
| Digital Airlock | The secure API bridge separating local OpenClaw operations from cloud-based AI. |
| Island Mode | Operation state where the Gateway manages all local smart home/network tasks completely offline. |
| Split-Ledger | Architecture separating private “Physical Truth” (local) from public logistical data (cloud). |
The values defined above are physically realized through the “Forge” provisioning process, where sovereignty is anchored to silicon.
2. The ‘Forge’ Protocol: Hardware Identity Anchoring
The “Forge” is the critical juncture where digital sovereignty is anchored to physical silicon. This process is the cornerstone of the DeReticular security model, replacing vulnerable cloud-based accounts with a physical, account-less identity. Technicians are responsible for the permanent bonding of hardware to its cryptographic root.
Identity Anchoring Instructions
- Hardware Pull: Retrieve a raw, unconfigured DER-SG-CORE base node from bulk inventory.
- Secure Connection: Connect the unit to the secure, air-gapped provisioning intranet.
- OS Flash: Flash the latest stable build of SW-RIOS-CORE (Rural Infrastructure Operating System) to the internal IC-STR-512GB storage.
- TPM 2.0 Initialization: Initialize the IC-SEC-TPM2 Hardware TPM 2.0 Cryptoprocessor to create a secure, immutable key enclave.
- RF Fingerprinting: Execute the unique Radio Frequency (RF) Fingerprinting sequence for the IC-WIFI-6E and IC-LORA-TX radios. Note: This is a destructive and permanent process that binds the networking array to the device’s physical signature.
- Split-Ledger Genesis: Create the localized Split-Ledger genesis block. This ensures all future “Physical Truth” data remains local to this specific hardware.
Identity Handshake Mechanism
Upon successful anchoring, the provisioning server shall write a one-time cryptographic handshake key to the SEC-NFC-BDG-01 (NFC-Enabled Sovereign Badge Setup Card).
Security Requirement: This card is the unique root admin passkey. This account-less identity model is designed to eliminate centralized database vulnerabilities. Identity is a physical truth, not a stored credential.
——————————————————————————–
3. Hardware Architecture & System Specifications
The Sovereign Gateway utilizes the “Premium Silicon Sentry” architecture. Technicians must handle these components as high-density AI inference appliances, not standard consumer routers. The move to a 0dB passively cooled extrusion chassis is a tactical choice for residential permanence.
Hardware Breakdown (Level 1 & 2)
- The Compute Layer (SUB-PCBA-MAIN): Features a modified IC-CPU-M4-MOD (Modified Apple M4 SoC) optimized for 5W idle power draw. It is supported by IC-RAM-16GB (16GB LPDDR5X Unified Memory) and IC-STR-512GB (512GB NVMe Flash).
- The Networking Array (SUB-PCBA-NET): Known as “Trifi Wireless,” this PCBA integrates IC-WIFI-6E (Wi-Fi 6E Tri-band) and IC-LORA-TX (Sub-GHz LoRaWAN) for local mesh “canopies.” Physical I/O includes dual CON-ETH-RJ45 2.5GbE ports.
- Expansion Capability: The base node is compatible with the Nomad Link Lite add-on baseplate for LTE/Starlink failover bonding.
- Chassis & Thermals (SUB-CHAS-ALUM): An CHS-ALUM-EXT (Anodized Aluminum Extrusion) shell acting as a primary heatsink for silent, fanless operation.
Software Payload Verification
Technicians must verify that the following pre-flashed software components are active:
- SW-RIOS-CORE: Rural Infrastructure Operating System.
- SW-AGNT-OCLAW: OpenClaw Agentic Framework Runtime.
- SOV-AUTO-DEV: The “DevOps Sovereign” agent (Autonomous network self-healing).
- SOV-AUTO-EXEC: The “Sovereign Executive” (User-facing Chief of Staff/UI Backend).
- SW-APP-VAULT: “Vault Warden” (Local volumetric and multispectral video processor).
WARNING: The integration of the modified M4 SoC and military-grade TPM 2.0 encryption subjects this device to strict international trade oversight.
——————————————————————————–
4. Regulatory Framework: ITAR/EAR and OFAC Compliance
The Sovereign Gateway is classified as a dual-use technology subject to ITAR/EAR controls due to its advanced AI inference capabilities and high-level encryption. Compliance is a non-negotiable blocker for all shipping activities.
Compliance Verification Protocol
The Warehouse Management System (WMS) acts as the hard blocker for fulfillment. No pick-ticket shall be generated until the following are satisfied:
- WMS Automated Scrub: Shipping addresses are cross-referenced against global export control lists and OFAC sanctions.
- Regulatory Oversight: All cleared orders must be audit-ready for review by the Export Compliance Officer (A. HAYES).
Risk Mitigation
Failure to maintain these protocols or any mismanagement of open-source vulnerabilities (specifically referencing the CVE-2026-25253 supply chain vulnerability in the OpenClaw framework) constitutes a catastrophic risk to DeReticular’s “unbreakable privacy” reputation. Technicians must ensure all units are flashed with patched versions of SW-AGNT-OCLAW.
——————————————————————————–
5. Fulfillment Workflow: Kitting and Secure Logistics
Fulfillment is the final stage in maintaining the “Chain of Custody.” High-value signatures are required for all deliveries to prevent the compromise of AI hardware.
Assembly and Kitting Instructions
- Assemble the DER-PKG-BX-01 (Retail Packaging) with the DER-PKG-INS-01 (Molded Pulp Tray).
- Insert one (1) provisioned DER-SG-CORE (Sovereign Gateway Base Node).
- Include Accessory Kit:
- ACC-PWR-CBL-1.5: 1.5m Braided Power Cable (USB-C to Barrel).
- ACC-PWR-GAN-60: 60W GaN Power Adapter.
- ACC-ETH-CAT7-2M: 2m Cat 7 Shielded Ethernet Cable.
- Place the paired SEC-NFC-BDG-01 (NFC Sovereign Badge Card) at the top of the tray for immediate visibility.
Security Sealing Protocol
Technicians must apply two (2) PKG-TPE-HOLO (Tamper-Evident Holographic Security Seals) to the box. These seals must be intact; the customer is instructed to reject any unit where the “VOID” indicator is visible.
——————————————————————————–
6. Lifecycle Management: Onboarding and Data Destruction
The “Zero-Touch” philosophy ensures data sovereignty persists from initial activation through the end-of-life Return Merchandise Authorization (RMA) process.
The “Sovereign Handshake” Onboarding
Setup is entirely offline and account-less:
- Activation: The user taps their smartphone to the SEC-NFC-BDG-01 card.
- Badge Minting: A cryptographic token is minted directly into the user’s Apple or Google Wallet via a local Wi-Fi Direct/Bluetooth handshake.
- Remy Bridge: If the user elects to use cloud logistics, they must provide their own API keys for Google Project Remy, which are then secured behind the “Digital Airlock.”
RMA and Data Shredding Protocol
To guarantee absolute privacy, returned units must undergo immediate cryptographic destruction:
- Hardware Jig Requirement: Upon receipt of an RMA, technicians shall connect the unit to the proprietary hardware jig.
- TPM Wipe: The jig triggers the UI-BTN-RST (Physical Hardware Reset Pin Mechanism).
- Cryptographic Shredding: This process physically and permanently shreds the TPM 2.0 encryption keys.
- Result: All local data (Vault Warden feeds, mesh logs, and personal settings) is rendered into unrecoverable cryptographic noise. Bare-metal re-flashing is only permitted after this step is verified.
Final Conclusion
This end-to-end protocol ensures that the Sovereign Gateway remains a trustless, impenetrable node. By following these procedures, we ensure that Big Tech never sees inside the home, and the DeReticular mission of absolute physical and digital sovereignty is upheld.